

Kubic by Konic
Agentic coding, in your control.
Kubic is an open-source coding agent for the terminal, engineered for organizations that must govern how AI changes their code: every action is visible, every change is reversible, and every policy is enforced from the top down.
- License
- MIT
- Runtime
- Node 22.19+
- Models
- Any provider
- Install
- npm i -g kubic
Enterprise, in the terminal
Every control, where the work happens.
- 01
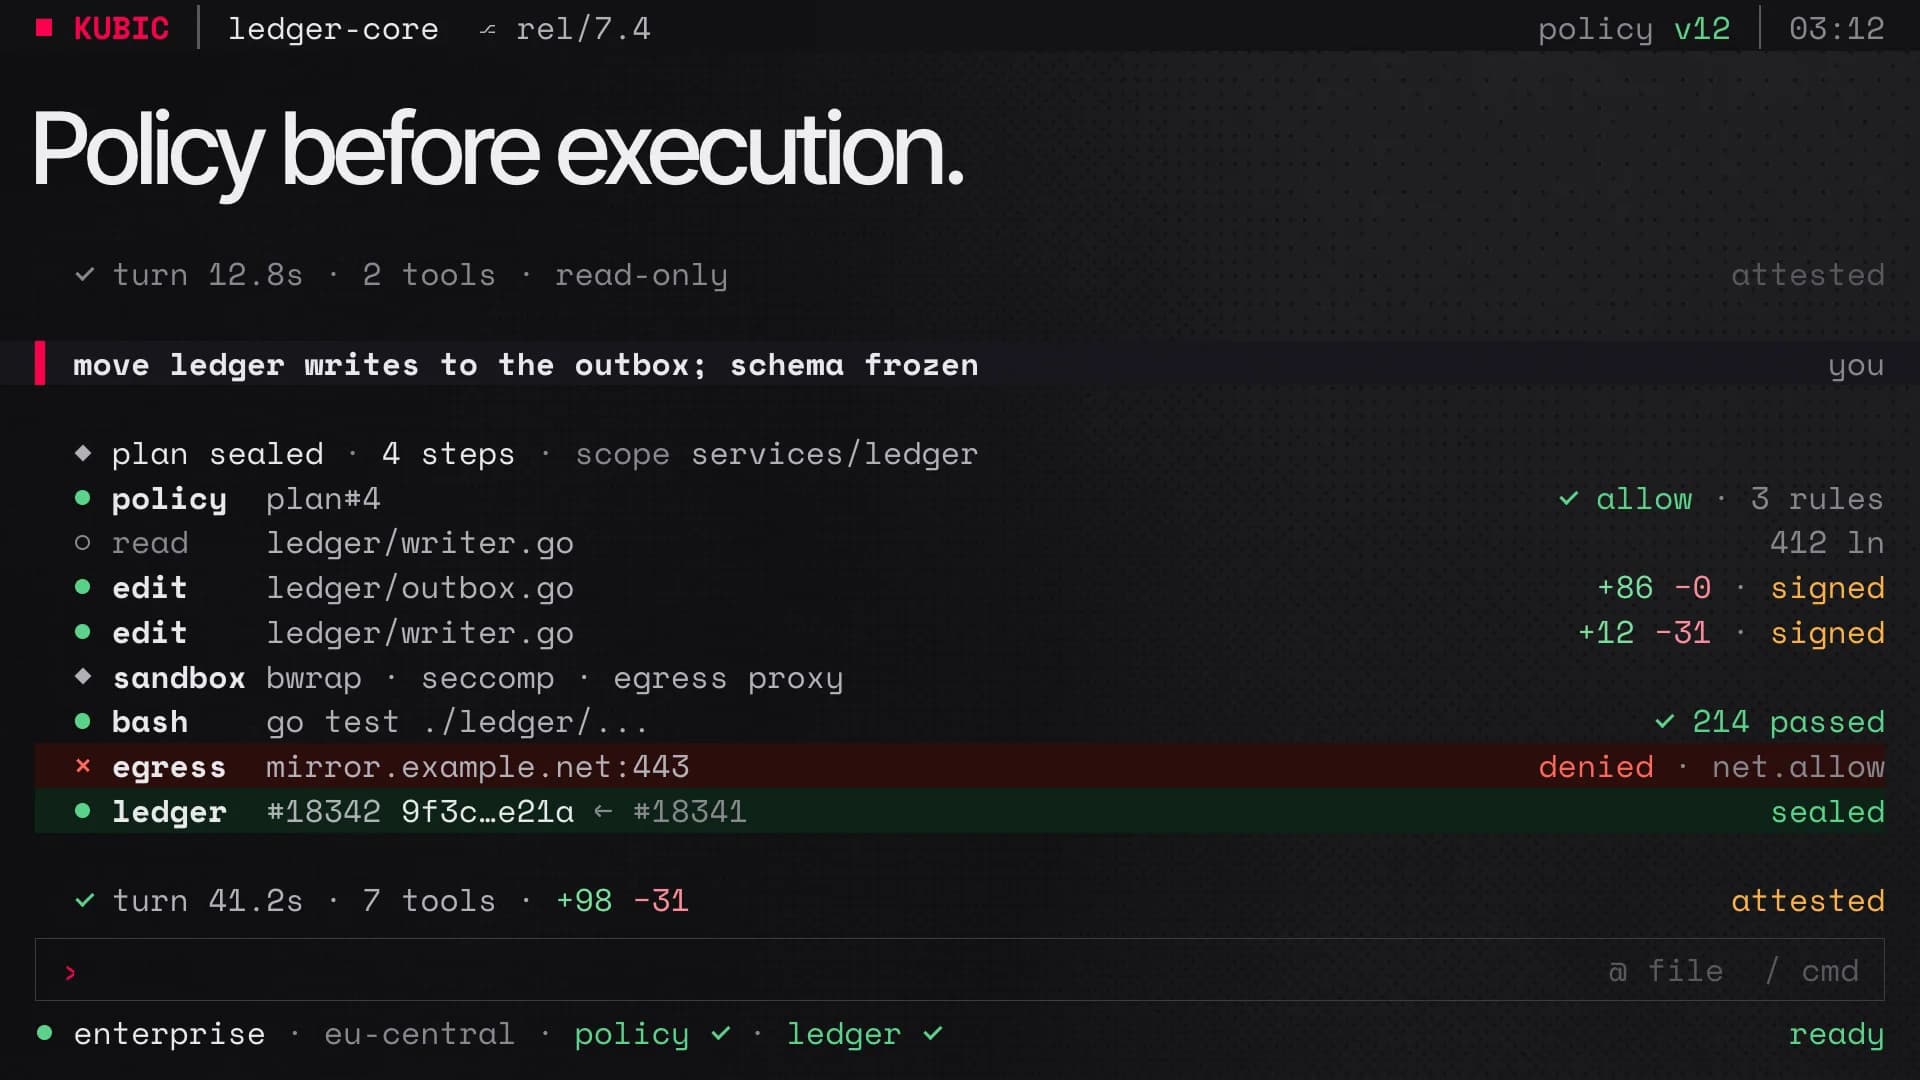
Policy before execution.
Every plan is evaluated against the organization’s managed policy before a single tool runs. The policy decides which models, providers and tools a session may use, where it may write and which hosts it may reach; users, repositories and the model itself can narrow it, never widen it.
- Highest-precedence policy layer, optionally signed
- Allowed and denied tools, network and filesystem policy
- kubic policy explain names the layer behind every decision
- 02
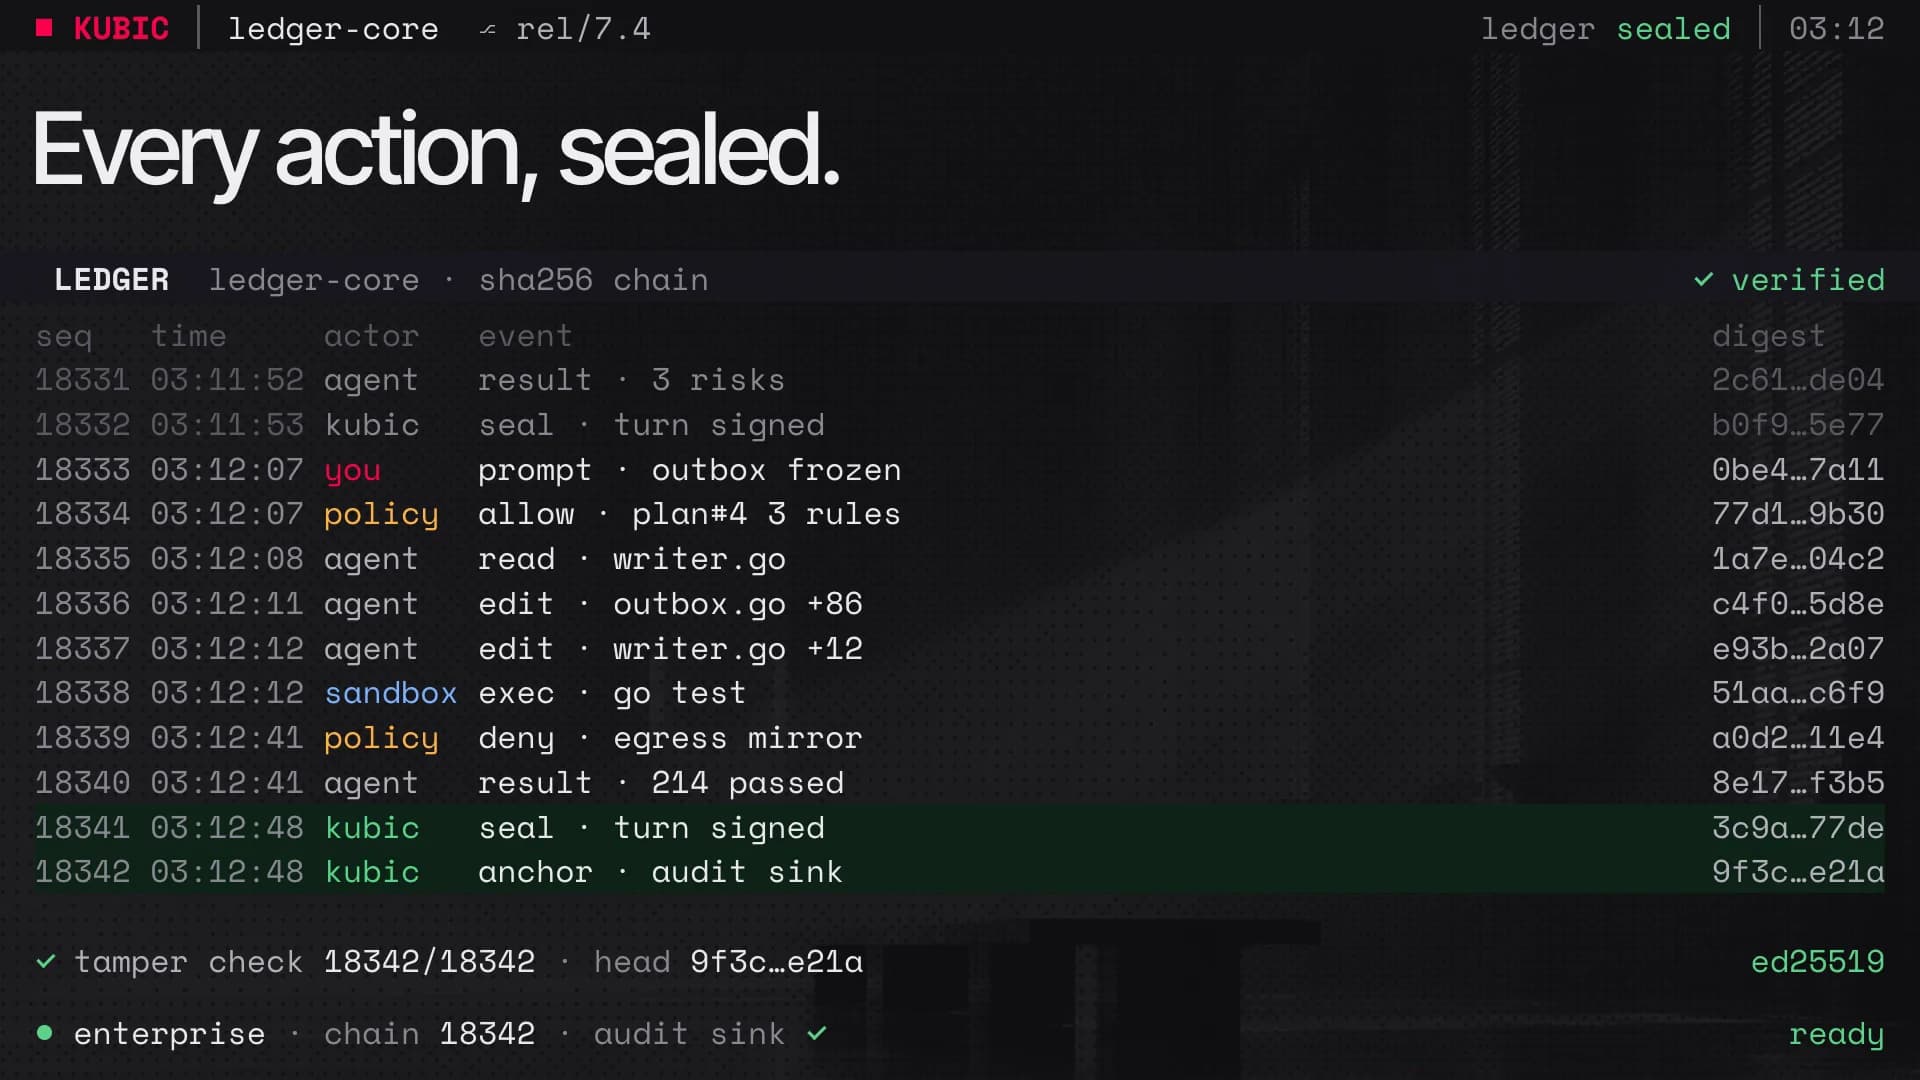
Every action, sealed.
Each prompt, tool call, approval and result is written to an audit ledger in which every record carries the hash of the one before it. Editing or removing a record breaks the chain, and kubic audit verify reports exactly where.
- Hash-chained, tamper-evident audit ledger
- Delivered to syslog, HTTPS or OpenTelemetry collectors
- Each record names the session and the model that acted
- 03
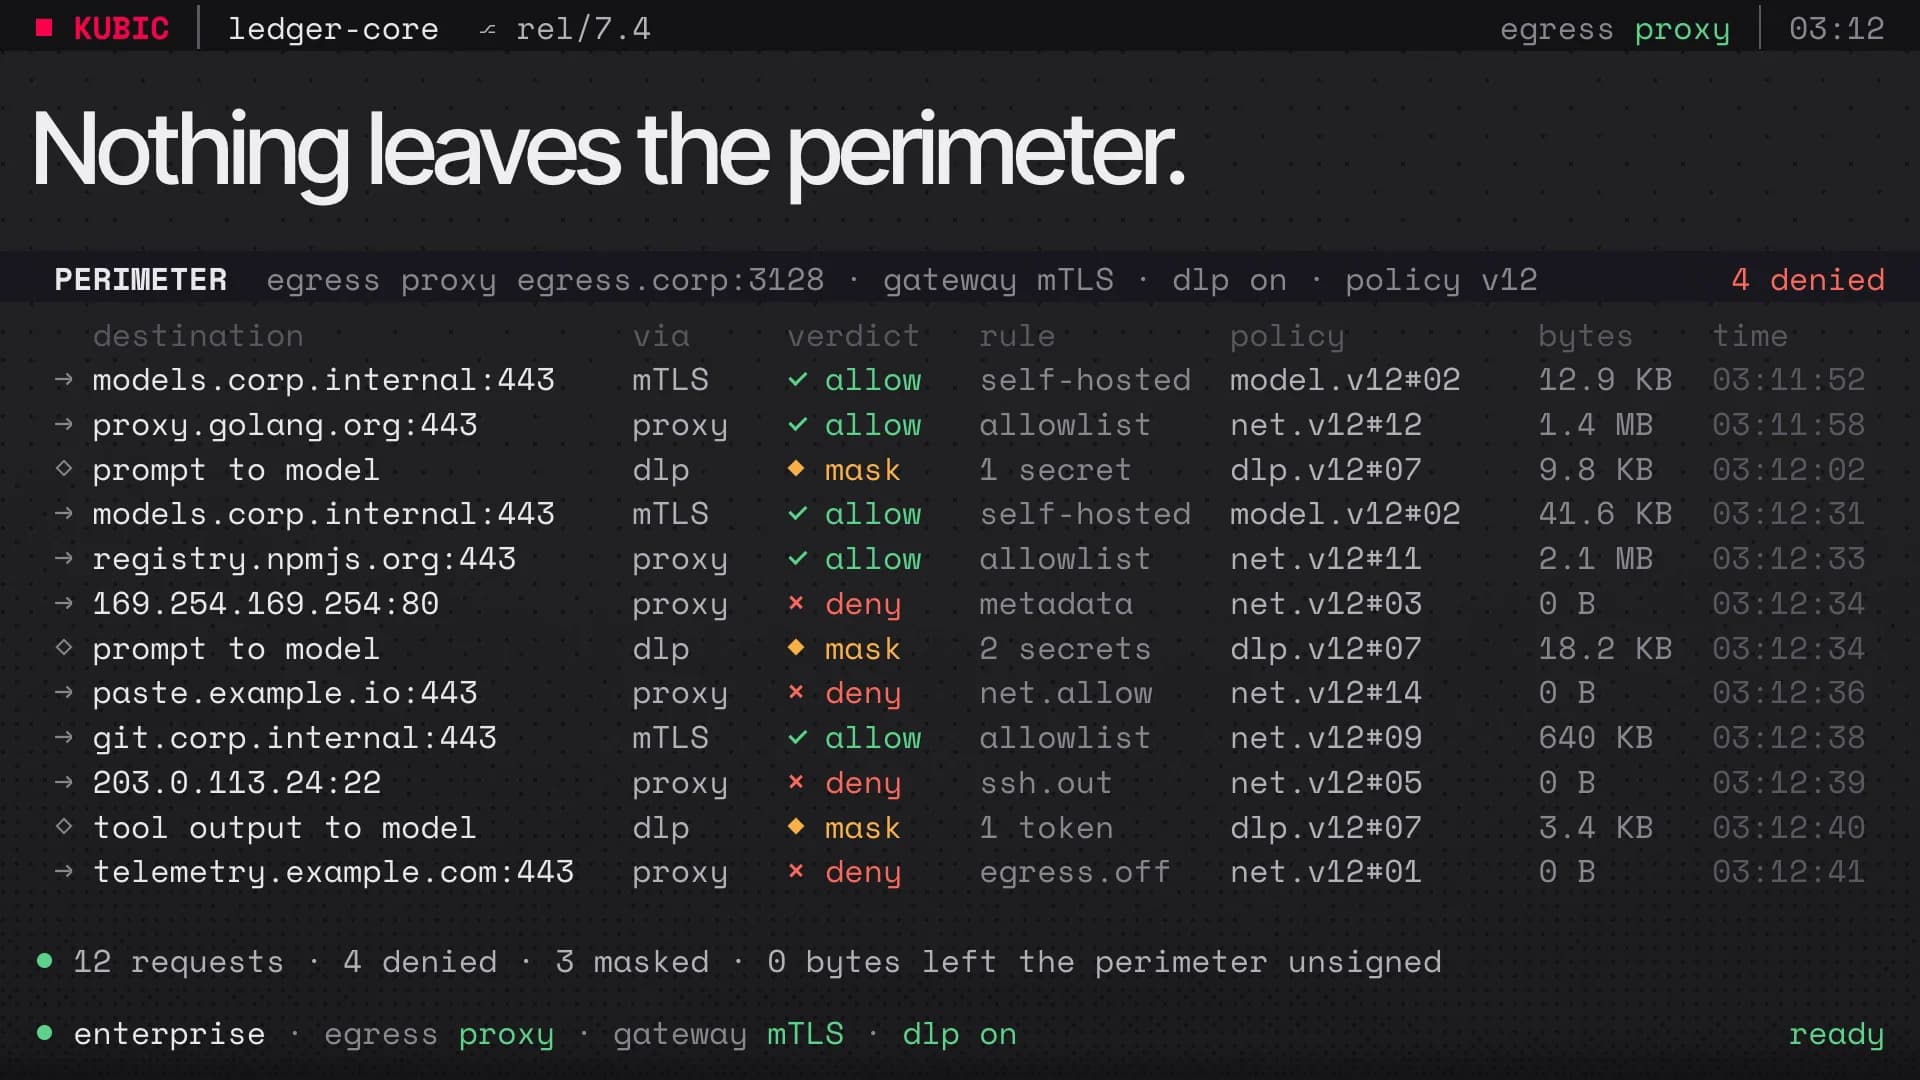
Nothing leaves the perimeter.
Outbound traffic from agent commands passes through an egress proxy that admits only the domains policy allows. Secrets are masked before tool output reaches the model, and provider keys never reach the processes the agent starts.
- Egress proxy with a domain allowlist
- Redaction of sessions and of tool output before the model reads it
- Seatbelt or bubblewrap sandbox for agent commands
- 04
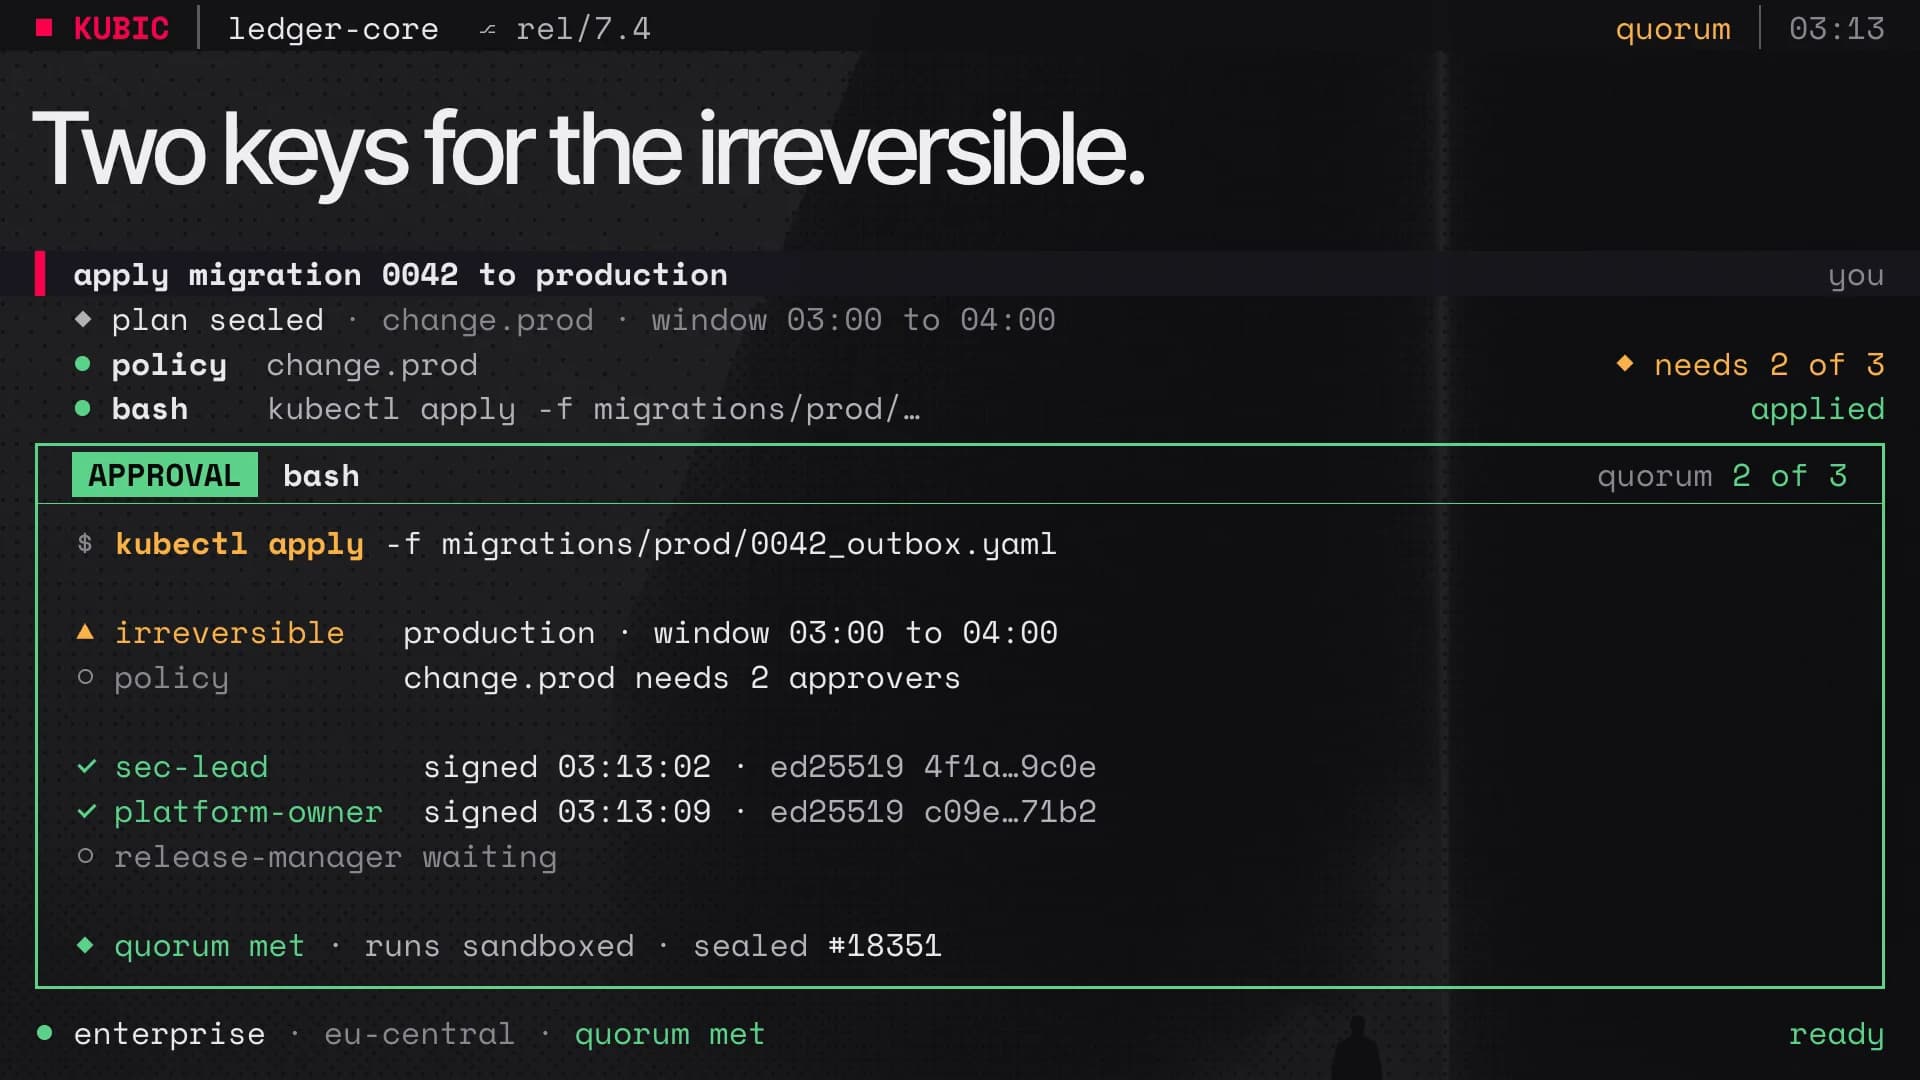
Two keys for the irreversible.
Irreversible operations stop at an approval card that states what the command does and why it was challenged. Decisions can be routed through an approval broker to the people accountable for them, and in the enterprise edition a production change can require more than one signer.
- Destructive, deploy and privilege commands are challenged before they run
- Approval broker and pre-approval files for headless runs
- Multi-party sign-off for production changes (enterprise edition)
- 05
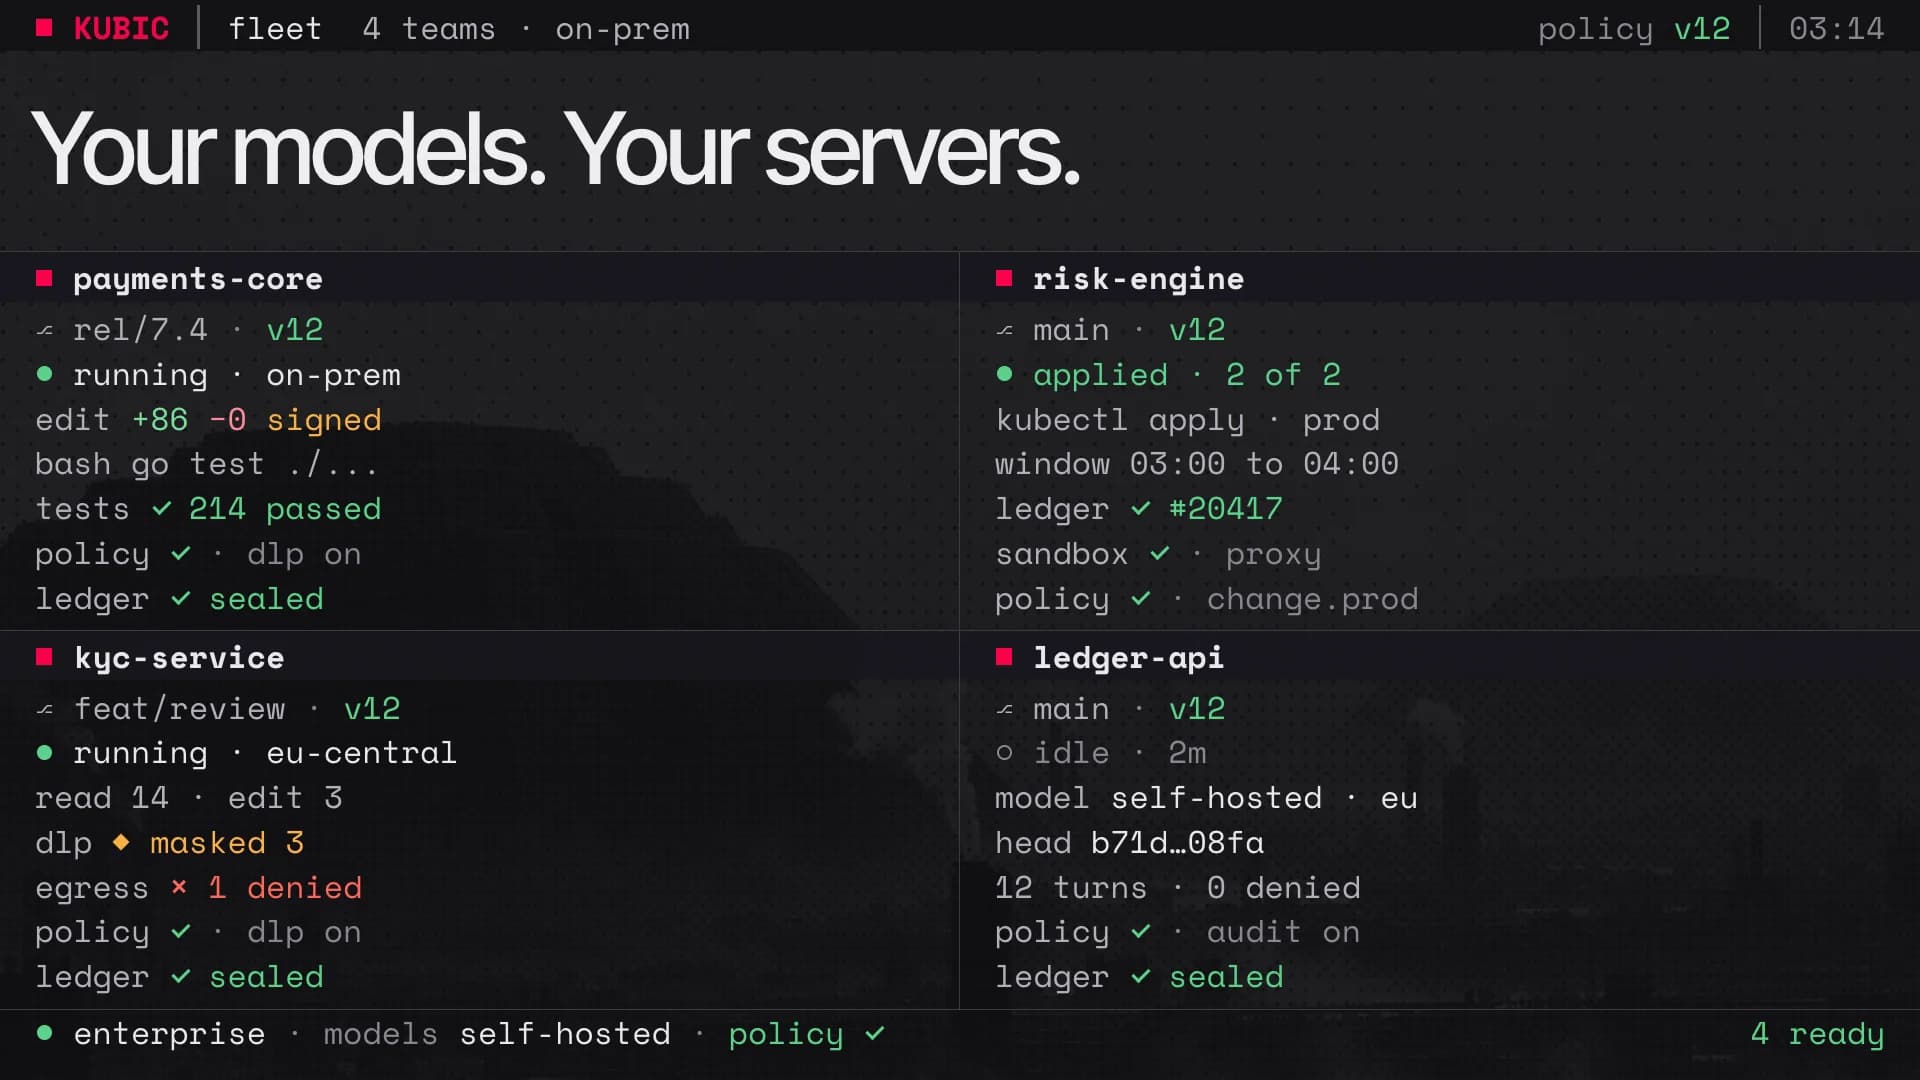
Your models. Your servers.
Kubic runs against the models and infrastructure the organization chooses: a commercial provider, a regional endpoint, or a model served on its own hardware. Every team works under the same policy version, with the same ledger and the same perimeter, wherever its sessions run.
- Any provider, or any OpenAI-compatible endpoint you host
- Provider regions with fallbacks, keys in the system keychain, OIDC in CI
- One policy and one audit trail across every team
Open-source core
Built for the engineer at the keyboard.
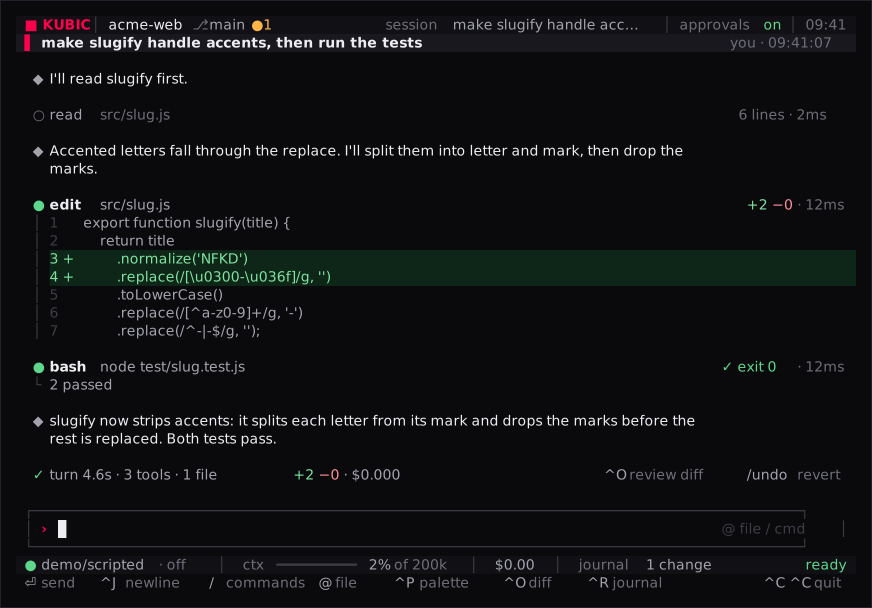
The enterprise controls sit on an open-source agent that engineers choose to use. These are recordings of the Kubic TUI as it ships today.
A session, step by step
Each read, edit and command appears as it happens, with the model, context, spend and journal in the status line.
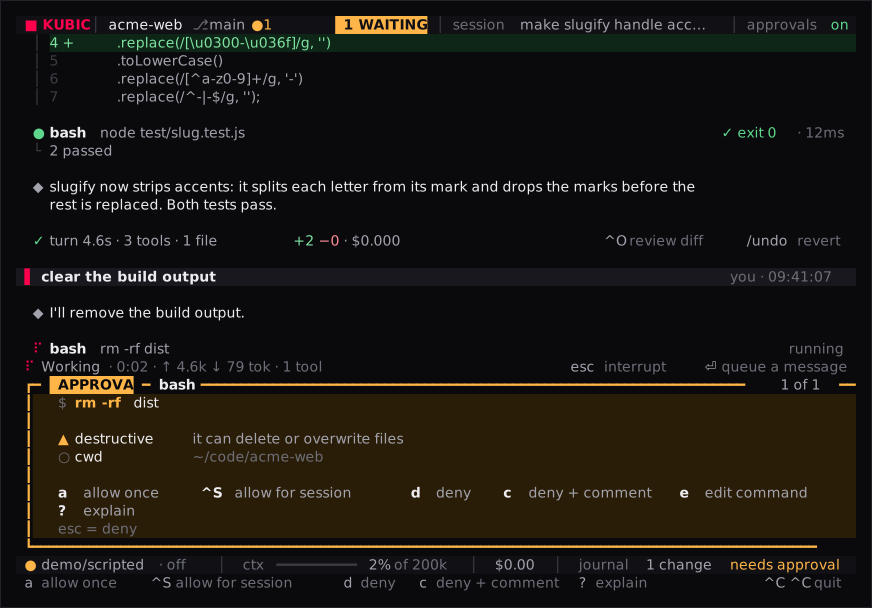
Approvals in the terminal
Allow once, allow for the session, deny, deny with a comment, or edit the command before it runs.
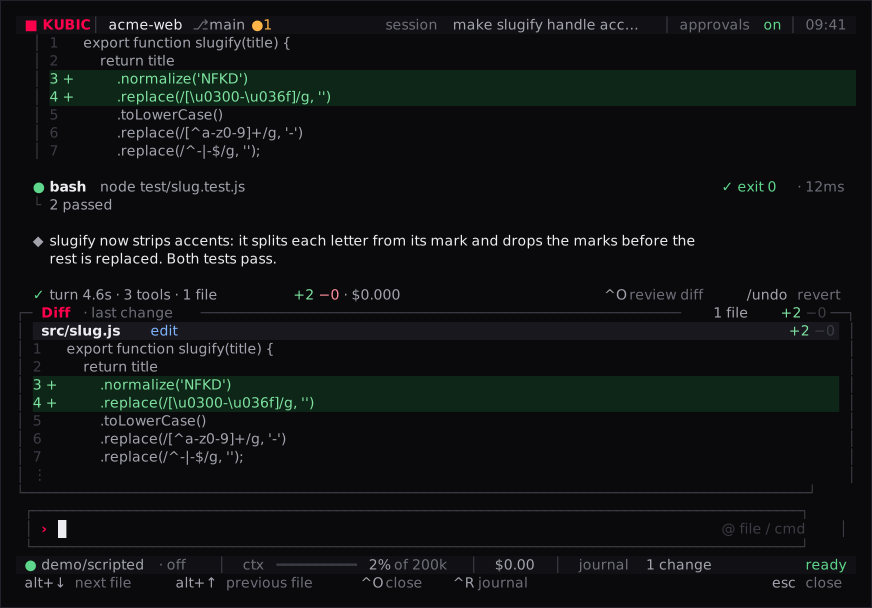
Review and undo
Ctrl+O shows the last change, Ctrl+R the session journal, and /undo restores a turn with or without git.
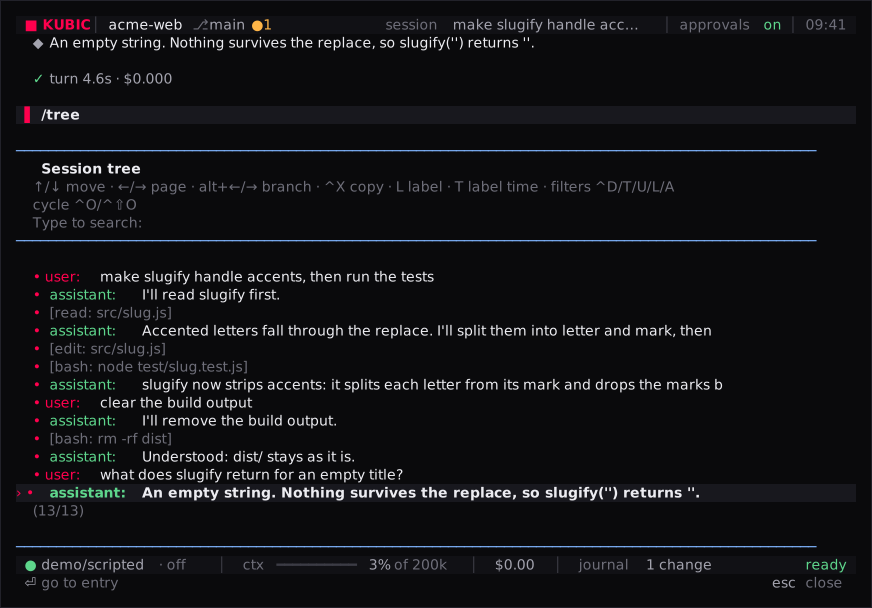
Sessions that branch
/tree lists every prompt, tool call and answer, and branches from any of them without losing the original line.
For the enterprise
Governance that holds at every layer.
An administrator sets policy once, in a managed configuration that takes precedence over every user, repository and model. Lower layers can only make it stricter.
Managed, signed policy
Allowed models, providers and tools, network and filesystem policy, set in a managed layer that can be signed so a replaced file is refused. kubic policy explain names the deciding layer for any value.
Tamper-evident audit ledger
Every record is hash-chained to the one before it and kubic audit verify walks the chain. Records are delivered to syslog, HTTPS or OpenTelemetry collectors through a spool.
Spend caps and cost reporting
Per-run and per-day caps, where the lowest value set by any layer wins. kubic cost reports spend by user, team, model and day, with CSV export.
Data loss prevention
Provider keys never reach tool processes, live keys are scrubbed from what a run stores and prints, and redaction can scan sessions or tool output before the model reads it.
Sandbox and egress control
An opt-in Seatbelt or bubblewrap sandbox confines bash to the workspace, away from credential paths and network sockets. An egress proxy limits traffic to allowed domains.
Repository trust
A repository’s own configuration, roles and instructions load only after kubic trust, and a change asks again. Under a restricted project policy a repository cannot widen approvals.
Identity, regions and networks
Provider keys in the operating system keychain, OIDC workload identity in CI, provider regions with fallbacks, and the system certificate store for TLS-inspecting corporate proxies.
Automation and admin hooks
Headless runs for CI and a GitHub Action, with organization-defined hooks before and after every tool call and at the end of each run.
Models
Any model, including your own.
Kubic works with Anthropic, OpenAI, Google, Amazon Bedrock and OpenRouter, or with any OpenAI-compatible endpoint you host. Paired with a Konic model deployed on your infrastructure, source code and prompts stay inside your network. Policy decides which models a team may use.
- Konic
- Anthropic
- OpenAI
- Amazon Bedrock
- OpenRouter
- Self-hosted
Get started
npm install -g kubic
export ANTHROPIC_API_KEY=...  # or OPENAI_API_KEY, GEMINI_API_KEY, ...
kubic                         # the first launch picks a default model
Requires Node 22.19 or later. npx kubic runs it without installing, and /undo puts any turn back.
Open-source core
The Kubic agent and TUI: any model, approvals, the change journal, branching sessions, the sandbox, managed policy, audit sinks and spend caps.
View on GitHubEnterprise and industry editions
The same core, deployed and supported by Konic for regulated organizations, with multi-party approvals, fleet-wide governance and Konic models served on your own infrastructure.
Talk to usKubic FAQ
Questions we get about Kubic.
Kubic is Konic's open-source coding agent for the terminal. It reads code, edits files and runs commands with the model your organization chooses, records every change in a journal that can be reviewed and undone, and asks before anything risky runs.
The Kubic agent and TUI are open source under the MIT license, including managed policy, audit sinks and spend caps. Enterprise and industry editions add deployment, support and governance across teams, delivered by Konic.
Anthropic, OpenAI, Google, Amazon Bedrock and OpenRouter, and any OpenAI-compatible endpoint, including Konic models served on your own infrastructure. A managed policy can restrict which models and providers each team may use.
Every write is recorded in a change journal, including changes made through bash. The diff and journal panels show what changed, and /undo or kubic undo restores a turn whether or not the project uses git.
A managed policy layer sets allowed models, providers and tools, network and filesystem policy, data redaction, spend caps and audit sinks. It takes precedence over every user, repository and model, which can narrow it but never widen it, and it can be signed so a replaced file is refused.
Not by default. Kubic runs in-process with the engineer's own authority. The opt-in Seatbelt or bubblewrap sandbox confines the bash tool's commands, and the egress proxy limits where they connect; file tools rely on workspace confinement and approvals.
No coding agent can promise that, and Kubic does not. Injected instructions can reach the model; approvals, the journal, admin hooks, the sandbox and the egress proxy limit what they can make Kubic do. Command detection is lexical and not complete, which is why the sandbox and the proxy do not depend on reading the command.
Yes. kubic run executes the same session headless, and the repository ships a GitHub Action that runs Kubic on a pull request and posts the result. Challenged actions are answered by an approval broker or pre-approval files, or refused.
Bring Kubic to your engineering organization.
Start with the open-source agent today, or talk to us about managed policy, audit and on-prem models for your teams.